Title: The Brave New (Quantum) World
Abstract
Major advances across all the design stack of Quantum computing – algorithm, software, and hardware – has brought us to a realm where, it is impossible to ignore the effect of Quantum computing in the world around us. We will discuss two aspects of Quantum computing in this talk. First, efficient circuit design and automation challenges – and how we can borrow some knowledge from classical computing for that. We will conclude this part with case studies on experimental Quantum computers. Second, the most important practical threat from a large-scale Quantum computer is on public-key cryptography. This is countered by developing and standardizing Post-Quantum Cryptography (PQC) primitives. We will talk about various PQC candidates and the perils of migration to a Quantum-safe environment.
Bio
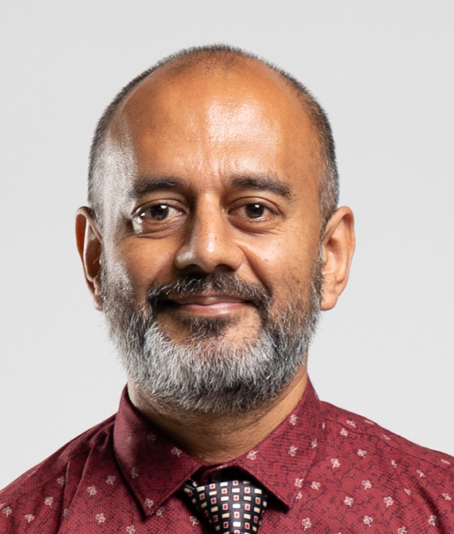
Anupam Chattopadhyay received his B.E. degree from Jadavpur University, India, MSc. from ALaRI, Switzerland and PhD from RWTH Aachen in 2000, 2002 and 2008 respectively. From 2008 to 2009, he worked as a Member of Consulting Staff in CoWare R&D, Noida, India. From 2010 to 2014, he led the MPSoC Architectures Research Group in RWTH Aachen, Germany as a Junior Professor. Since September 2014, Anupam was appointed as an Assistant Professor in College of Computing & Data Science, NTU, where he got promoted to Associate Professor with Tenure from August, 2019. In the past, he held visiting positions at Politecnico di Torino, Italy; EPFL, Switzerland; Technion, Israel; Kyoto University, Japan and Indian Statistical Institute, Kolkata.
Anupam currently heads a team of 20+ researchers, overseeing projects in computer architectures, security, design automation and emerging technologies. His research advances have been reported in more than 300 conference/journal papers (ACM/IEEE/Springer), multiple research monographs and edited books (CRC, Springer) and open-access forums.
Anupam regularly serves in the TPCs of top conferences (DAC, DATE, ICCAD, ASP-DAC, CHES), reviews journal/ conference articles and presented multiple invited seminars/tutorials in prestigious venues. He is an Associate Editor of IEEE TCAD, IACR CHES, ACM TECS, served as the Associate Editor of IEEE ESL, lead editor of Springer Handbook of Computer Architectures, and editor of Springer book series on Computer Architecture and Design Methodologies. He is fellow of JSPS, fellow of Intercontinental Academia, senior member of ACM and senior member of IEEE.
Awards
Nanyang Award for Innovation and Entrepreneurship, 2025.
Best Poster Award in AsiaCCS, 2025.
Best Paper Award in Cryptographic Hardware and Embedded Systems (CHES), 2025.
Best Paper Award in VLSI-SoC Conference, 2024.
ACM TODAES Distinguished Reviewer, 2022.
IEEE CEDA Distinguished Lecturer, 2022-2023.
Best Paper Award in International Conference on Security, Privacy and Applied Cryptographic Engineering (SPACE), 2020.
Nripendra Nath Biswas Special Mention Recognition in ACM/IEEE VLSI Design Conference, 2020.
Nominated for Best Paper Award in ACM/IEEE VLSI Design Conference, 2018.
Nominated for Best Interactive Presentation (IP) Award in ACM/IEEE DATE, 2016.
Recipient of Borchers’ plaque for outstanding PhD dissertation from RWTH Aachen, 2008.